Wednesday, July 07, 2021

Meraki MX64 Review


I have had the good fortune in being able to have a look at the Meraki MX64 router/security appliance from Cisco.  Since I use PFSense I was interested in see what this locked down proprietary appliance was all about.  At my work we are using Meraki Switches and have been very happy with them, they are easy to setup, configure, manage, and the web based management system gives you a wonderful single pane of glass to view everything.  I was interested in seeing if the router was as easy to setup and manage.

Like all Cisco Meraki products, you add the device by going to the Network-Wide menu and go add device as shown below.


Then press the claim button on the right most side of the screen across from the search box.


You will get a popup asking for the serial number of the device or the order number(s).


Then put in the serial number, if you don't have the order or email you can find the serial number located at the bottom of the device


After that you will need to add the license for the device which would come from your provider.  If you don't have a license you only have 14 days in which you will be able to use the device before getting a license.


Select "add another license"


Input the license provided by your provider.  Select the operation License more devices (as we are adding the router to our meraki cloud)


Once that is done you will have a few side bar menu called Security & SD-WAN if you didn't have a meraki router before.


After getting the device registered, it took a while for the dashboard to recognize it but to be fair I have it going to the internet though my PFSense firewall, it did eventually make a connection.  One thing I will note is it did come with a network preconfigured in the device probably supplied to our vendor when they sent it over at our request.  For example it would have came on a non configured vlan 192.168.0.1/24 setup with DHCP which I would already have on my meraki network.

After getting the device connected, The network setup is located under the Addressing & VLANs menu

By default the device comes in routed mode and single lan setting.


Configuring the MX64 for use with VLANS is pretty easy, change the lan setting to VLANs then add the VLASs using the "Add VLAN" button.  It is easy and very straight forward.  I have left the deployment settings the same but I changed the Single Lan Setting to VLAN and setup the following.

  1. Setup VLAN 1 with a subnet of 192.168.0.0/24 - MX IP 192.168.0.1 (DHCP Served By Meraki MX)
  2. Setup VLAN 2 with a subnet of 192.168.10.0/24 - MX IP 192.168.0.10 (No DHCP)
  3. Setup VLAN 3 with a subnet of 172.32.0.0/24 - MX IP 172.32.0.4 (No DHCP)
I then setup the ports

- WAN port goes to my LAB network 192.168.182.0/24 the MX has an ip of 192.168.182.50
- Lan 3 I have going to my laptop with 2 VLANs attached.  Lan 2 is setup as the NATIVE VLAN which has no DHCP Server 


When I plugged my laptop into port 3 which as a native vlan of VLAN2 which has no DHCP server on that network I got a 169 address.  When I changed my VLAN on my laptop to access VLAN 1; the output of ipconfig from my laptop where DHCP is being server by meraki mx I got the following:

PS C:\Users\Trevor Tye> ipconfig /all

Windows IP Configuration

   Host Name . . . . . . . . . . . . : Lenovo-P52s

   Primary Dns Suffix  . . . . . . . :

   Node Type . . . . . . . . . . . . : Hybrid

   IP Routing Enabled. . . . . . . . : No

   WINS Proxy Enabled. . . . . . . . : No

Ethernet adapter vEthernet (Default Switch):

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : No

   Autoconfiguration Enabled . . . . : Yes

   Link-local IPv6 Address . . . . . :(Preferred)

   IPv4 Address. . . . . . . . . . . : (Preferred)

   Subnet Mask . . . . . . . . . . . : 255.255.240.0

   Default Gateway . . . . . . . . . :

   DHCPv6 IAID . . . . . . . . . . . : 1006638429

   DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-23-4D-16-AA-48-2A-E3-1A-77-16

   DNS Servers . . . . . . . . . . . : fec0:0:0:ffff::1%1

                                       fec0:0:0:ffff::2%1

                                       fec0:0:0:ffff::3%1

   NetBIOS over Tcpip. . . . . . . . : Enabled


Ethernet adapter vEthernet (Internal Network):

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter #3

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes

   Link-local IPv6 Address . . . . . : (Preferred)

   Autoconfiguration IPv4 Address. . : 169.254.38.103(Preferred)

   Subnet Mask . . . . . . . . . . . : 255.255.0.0

   Default Gateway . . . . . . . . . :

   DHCPv6 IAID . . . . . . . . . . . :

   DHCPv6 Client DUID. . . . . . . . :

   DNS Servers . . . . . . . . . . . : fec0:0:0:ffff::1%1

                                       fec0:0:0:ffff::2%1

                                       fec0:0:0:ffff::3%1

   NetBIOS over Tcpip. . . . . . . . : Enabled


Ethernet adapter vEthernet (External Switch):

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Hyper-V Virtual Ethernet Adapter #2

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes

   Link-local IPv6 Address . . . . . : (Preferred)

   IPv4 Address. . . . . . . . . . . : 192.168.0.20(Preferred)

   Subnet Mask . . . . . . . . . . . : 255.255.255.0

   Lease Obtained. . . . . . . . . . : July 7, 2021 1:24:49 PM

   Lease Expires . . . . . . . . . . : July 8, 2021 10:42:26 AM

   Default Gateway . . . . . . . . . : 192.168.0.1

   DHCP Server . . . . . . . . . . . : 192.168.0.1

   DHCPv6 IAID . . . . . . . . . . . :

   DHCPv6 Client DUID. . . . . . . . :

   DNS Servers . . . . . . . . . . . : 192.168.0.1

   NetBIOS over Tcpip. . . . . . . . : Enabled


Wireless LAN adapter Wi-Fi:

   Media State . . . . . . . . . . . : Media disconnected

   Connection-specific DNS Suffix  . : optionkey.ca

   Description . . . . . . . . . . . : Intel(R) Dual Band Wireless-AC 8265

   Physical Address. . . . . . . . . : 18-1D-EA-2F-AE-59

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes


Wireless LAN adapter Local Area Connection* 3:

   Media State . . . . . . . . . . . : Media disconnected

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Microsoft Wi-Fi Direct Virtual Adapter #5

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes


Wireless LAN adapter Local Area Connection* 4:

   Media State . . . . . . . . . . . : Media disconnected

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Microsoft Wi-Fi Direct Virtual Adapter #6

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : No

   Autoconfiguration Enabled . . . . : Yes


Ethernet adapter Ethernet 2:

   Media State . . . . . . . . . . . : Media disconnected

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : TAP-Windows Adapter V9

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes


Ethernet adapter Bluetooth Network Connection:

   Media State . . . . . . . . . . . : Media disconnected

   Connection-specific DNS Suffix  . :

   Description . . . . . . . . . . . : Bluetooth Device (Personal Area Network)

   Physical Address. . . . . . . . . :

   DHCP Enabled. . . . . . . . . . . : Yes

   Autoconfiguration Enabled . . . . : Yes

PS C:\Users\Trevor Tye>


In my lab network I have a subnet of 192.168.1.0/24 on the static route I setup a route to go to 192.168.1.0 from 192.168.10.1.  For clarification my laptop is plugged into Port 3 on the switch which has a a native vlan of VLAN2 which has no DHCP services.  Below is the appliance status menu showing the connected ports.


I had set the virtual switch on my laptop to VLAN1, demonstrating that VLANs work because VLAN 1 is being served DHCP by Meraki MX.  The Static route I setup seems to be working as the ping test below shows pinging both the gateway and my workstation on the 192.168.1.0/24 network from 192.168.0.20

PS C:\Users\Trevor Tye> ping 192.168.1.1

Pinging 192.168.1.1 with 32 bytes of data:

Reply from 192.168.1.1: bytes=32 time<1ms TTL=64

Reply from 192.168.1.1: bytes=32 time<1ms TTL=64

Reply from 192.168.1.1: bytes=32 time<1ms TTL=64

Ping statistics for 192.168.1.1:

    Packets: Sent = 3, Received = 3, Lost = 0 (0% loss),

Approximate round trip times in milli-seconds:

    Minimum = 0ms, Maximum = 0ms, Average = 0ms

Control-C


PS C:\Users\Trevor Tye> ping 192.168.1.250

Pinging 192.168.1.250 with 32 bytes of data:

Reply from 192.168.1.250: bytes=32 time<1ms TTL=64

Reply from 192.168.1.250: bytes=32 time<1ms TTL=64

Reply from 192.168.1.250: bytes=32 time<1ms TTL=64

Reply from 192.168.1.250: bytes=32 time<1ms TTL=64

Ping statistics for 192.168.1.250:

    Packets: Sent = 4, Received = 4, Lost = 0 (0% loss),

Approximate round trip times in milli-seconds:

    Minimum = 0ms, Maximum = 0ms, Average = 0ms


The DHCP tab is nice as it shows the amount of IP's used and the uplink tab also gives some "nice to know information".


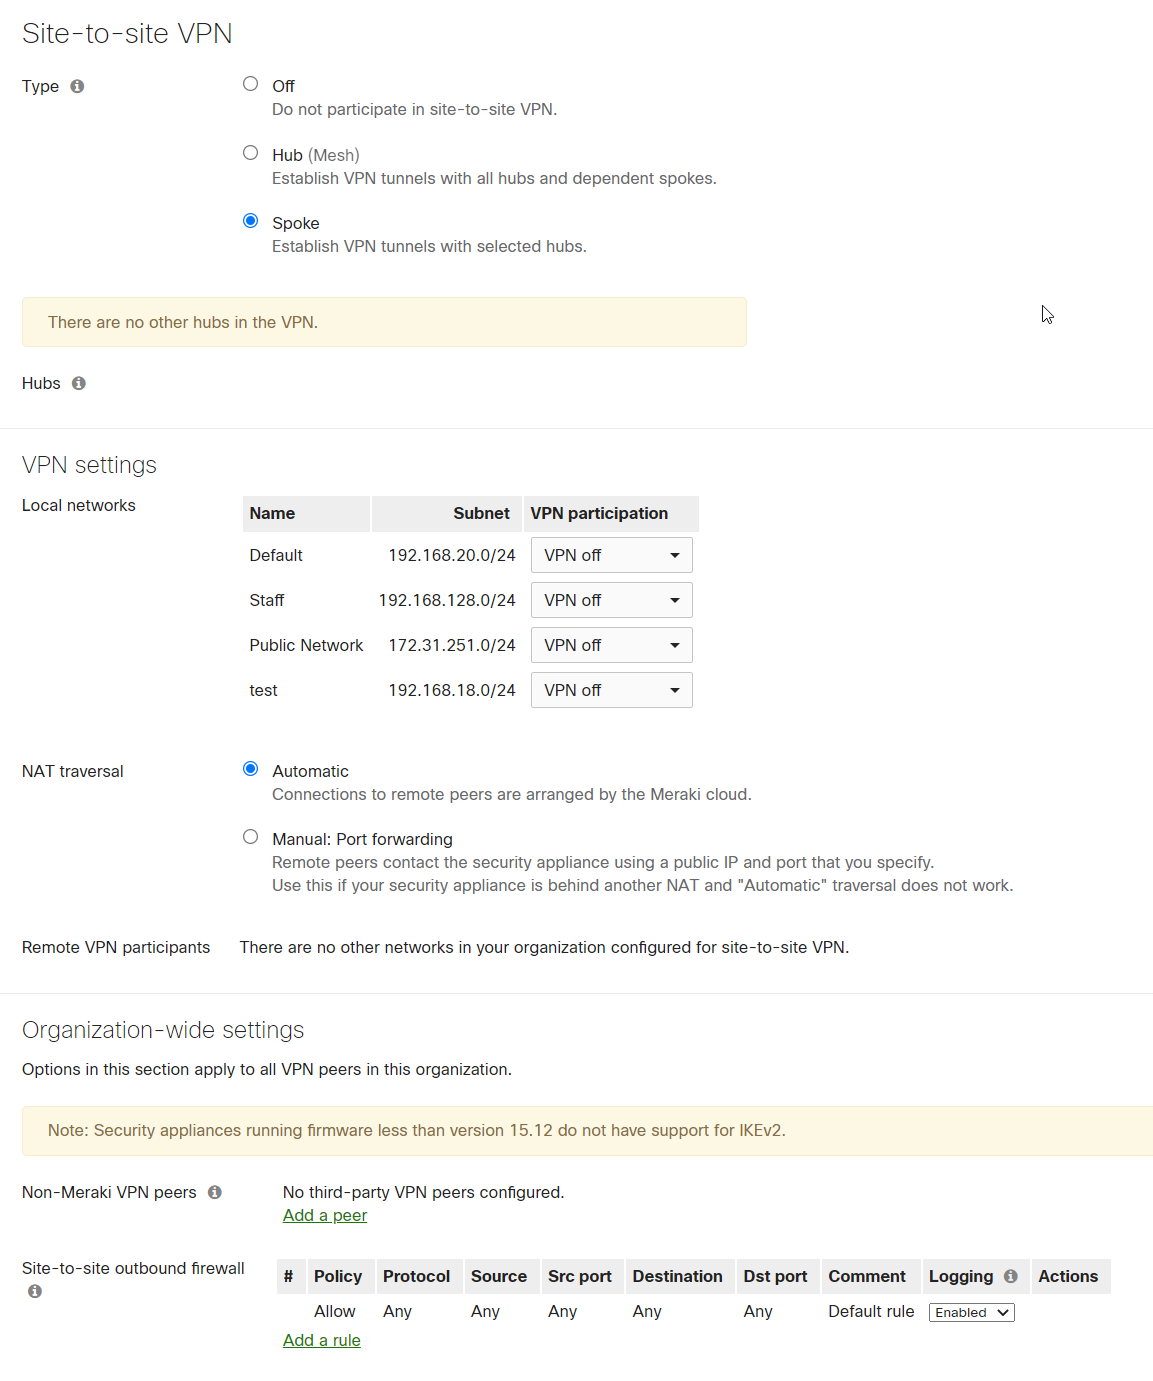
There are a lot of features I would like to play with but it looks like I would need multiple mx appliances, such as setting up the firewall rules, and VPN, it looks like it would be easy to do and setup.
Firewall:
VPN (Site 2 Site)


VPN Client


The Meraki MX comes with the typical router features such as URL allow/deny listing, content filtering, traffic shaping (with some nice defaults), but also has some nice integrations having quick access the the WiFi Splash page, VPN, threat detection (and Cisco Umbrella or use to be known as OpenDNS) and intrusion detection.  In my opinion this would be great to have if your a smaller business or franchise with lots of locations, a service management company, or an organization you are looking to reduce the load of your IT staff and/or your staff are not technically inclined and/or have a limited experience with routing, setting up VPN servers or are very familiar with firewalls with different VPNs.  In my lab this was very easy to setup, and get working, I find there is more power with PFSense, and this would be fantastic solution if your going all in.  That is the thing though you have to go all in on Meraki.  Depending on your budget, and what your organization is wanting to do it can be quite the asset.


Wednesday, June 30, 2021

How to fix crontab scripts that won't run on Ubuntu 20.04

I've setup what I like to call WOLS (Wake on Lan & Shutdown) servers for a while now; 10 years to be exact.  They are very handy and require little to no system resources; I usually set them up on Hyper-V systems but have also done it on KVM and VMware.  It is very handy if your wanting to schedule systems for auto on and off without buying a commercial server or software.  You also don't have to have it connected to your domain if you don't want it to be.  

I setup a new server on Ubuntu 20.04 for managing the WOL/Shutdown for a remote location and set it up just as I have done in the past; but something was wrong.  It wasn't working.  The system was not turning on or shutting off the systems it was suppose to be.

For the purposes of this post lets say we are going to run all of our scripts out of /scripts/cron

You can use crontab -e or sudo crontab -e to edit cron, I prefer to modify the /etc/crontab file myself.  So when I build my WOLS server and modify the crontab file it usually looks something like this.

After I install the the required tools, WOL, samba tools, etc I white list the, WOL ports, SAMBA and remote desktop/Remote Access ports access though the firewall on both the client and the server. You can also disable the firewalls, though I don't recommend that.

The Startup Script is a shell script called startup.sh and it looks like this


I have found that if I don't put it in the arp cache I tend to have problems if the system has been off for a while.

sudo arp -i -s $IPADDRESS $MACADDRESS #COMMENT

example:

sudo arp -i -s $192.168.0.6 #FF:CC:DD:33:22:00

Then send the WOL Packets

sudo -i -u $SERVERUSER -p $PASSWORD wakeonlan -i $IPADDRESS $MACADDRESS #COMMENT

example:

sudo -i -u serveradm -p password wakeonlan -i 192.168.0.6 #FF:CC:DD:33:22:00

so you use the server usename and password to run the wakeonlan to the ipaddress with the specified mac address. The same is true with the shutdown script but you are using net rpc and you put in the windows client username and password behind the -U in quotes with a % separating the username and password as shown below.

The shutdown script is also a shell script called shutdown.sh and looks like this


sudo -i -u $SERVERUSER -p $PASSWORD net rpc shutdown -I $ipaddress -U "windowsclientusername%password" -t -1 -f 
sudo -i -u serveradm -p password net rpc shutdown -I 192.168.0.6 -U "joedirt%mopboy5" -t 1 -f
With that done, then adding execute permissions to the files and call it a day, as all the scripts worked when I manually executed them. Unfortunately that wasn't the case.  Something changed in Ubuntu 16 that caused files with extensions to not execute.

After troubleshooting and doing some Googling, I found this post with a similar issue to what I was having.  When I did a ls you can see the scripts in the folder.


With my files definitely having execute permission I tried the run-part command 
run-part --test /scripts/cron 
and got the following result


Nothing.  Absolutely nothing listed in the test.  So I did as Pete Fretag suggested and copied my startup.sh and shutdown.sh with out an extension.


Now the startup and shutdown scripts show up in the test.


When I run the scripts using sudo run-part /scripts/cron they also execute where they did not before.

Tuesday, June 29, 2021

How to add and remove persistent routes in windows

So at one of my organizations satellite locations we changed the VPN connection for about a half dozen clients, which were accessible from my workstation for remote access/system administration.  This changed caused this access to break.

So to update and fix my access for this systems I had to reset my routing for the satellite networks.  I setup this access using persistent routes (as I wanted to keep access after a reboot).

I used route print to verify the connections that need to be purged before I add the new ones.

To do this user powershell or the cmd prompt and type the following 

route print

and press enter

You will see your Interface List then Active routes then Persistent routes.

Interface List

Active Routes

Persistent Routes

The persistent route I want to remove is the third line shown below, we will say the network is 192.168.1.0


So to remove the route In Powershell or CMD Prompt I type 

route delete 192.168.1.0


Then to add the new route there are few things I need to know before I add the new persistent route.  I will need to know my network and gateway, that the firewall has a VPN connection with pass rules for the network and the VPN's network.  So for this post let's say the firewall is configured properly but is not routing traffic automatically.  For this post lets say that my IP is 192.168.20.87 and my gateway is 192.168.20.1.  The VPN network I want to connect to is 192.168.8.1

So I type the following in the same prompt

route -p ADD 192.168.8.0 MASK 255.255.255.0 192.168.20.1


The -p will make the connection stay after a reboot, if you don't want it to stay remove the -p and you should be able to access the other network from the VPN.


Source 

https://www.howtogeek.com/howto/windows/adding-a-tcpip-route-to-the-windows-routing-table/

Modifying Network SMB (Samba) Passwords

I had an issue with papercut where a SMB connection path was saved with the wrong username and password allowing higher then wanted privileges.  To change the user to one with lower privileges you can use the Manage Network Passwords from control panel.

 Type Manage Passwords in the windows 10 search


When open select the credential you want to modify.  In my case the second one highlighted in green.  Hit the dropdown to edit the settings.


When you hit edit, you will get a dialog with the name/ip of the server and then you can update the username/password as shown below.


Then hit save.  Once you do that if you put your $username and $password in properly, and try to access the network resource over SMB in explorer \\$server\ you should have full access (according to the user permissions that are granted to you by the server) as shown below


Tuesday, May 25, 2021

Meraki Switches and in accurate dashboard data, RTSP and STP errors

I like meraki switches, they are easy to manage, troubleshoot, and diagnose problems.  However one issue that recently occurred; which was quite odd where a switch in my meraki stack was showing ports as being blocked but were not.  As shown in the image below, Ports 3, 4, 14 and 18 were showing as being disabled.

I reboot the switch (off hours of course!), tried changing ports for connected devices, changing RTSP and STP settings and it did not resolve the issues the switch was having.  The switch continued to show with the rtsp forwarding was disabled on certain ports, stp discards and the dashboard display would not update.  Though some ports did show rtsp forwarding properly when viewing the details some ports are stuck in a disabled state such as port 18 on the diagram above.

What did fix the issue was rebooting a root switch.  As shown in the diagram below, I have the firewall going to a 1U switch, but then I have that switch going into a Meraki Stack.  

I rebooted each switch in the stack one at a time, but it didn't fix the issues with the switch in the stack.  When I rebooted the root switch connected between the firewall, and the stack and the troublesome switch had updated it's dashboard and the non-working ports in the switch started working.  Since meraki switches are pretty integrated it could be a pathing issue was resolved with the reboot of the root switch (even though technically in meraki software display the root switch was another switch).  Having a defined layer 3 setup might have prevented this issue; as for now if your are encountering this kind of issue follow the pathing up the chain and out to the internet rebooting any switches that are along that chain.


Wednesday, May 05, 2021

How to upgrade your linux server

How do you do an in place upgrade on a older Linux Server and why would you want to.  Well why you would want to is obvious, security patches, and giving longer life to the server on the newer software; that is a good reason.  With browsers being constantly upgraded, along with security issues being found every other day it seems, staying up to date is just a good idea.

So how do we stay up to date?

Typically, if you have been staying up to date you will eventually get prompted to do an upgrade to an newer version of linux at some point.  All the following commands will need to be run as root (sudo).


sudo apt-get update

Downloads package information from all configured sources.  Running this command keeps your package information up-to-date

sudo apt-get upgrade

This command only upgrades.  The upgrades are only upgrades available to the platform, as defined in /etc/apt/sources.list or in /etc/apt/sources.list.d/.  This upgrades your packages, not your OS and it will not remove packages.

sudo apt-get dist-upgrade, 

Intelligently installs or removes packages as needed.  This command has a smart conflict resolution system.  The system attempts to upgrade the most important packages, at the expense of those deemed less important.  This command will also delete software if it is required to complete the upgrade process.

sudo apt-get autoremove

Removes packages that were automatically installed because another package required them but, if they are no longer needed this command removes them.

sudo apt-get autoclean

Clears the local repository of retrieved package files, but it only removes files that can no longer be downloaded and are virtually useless. It helps to keep your cache from growing too large

sudo do-release-upgrade

The do-release-upgrade command will upgrade the system from one release to another. This is the command you want if you want to upgrade from Ubuntu 18.04 to 20.04.  NOTE:  The system must be fully upgraded to run. use the apt-get upgrade, followed by sudo apt-get dist-upgrade commands before running the do-release-upgrade command.


Fix a windows network printer that is offline

How to fix a network printer that get's installed and shows offline. By default SNMP is set to public, so when you are installing a netw...