Showing posts with label Linux. Show all posts

Thursday, July 23, 2026

Crontab changes in Linux 26.04 vs previous versions

I use a small Linux server to control the turning on and shutting off our client stations with crontab.  The system I typically use is Ubuntu Server running on Hyper-V, I setup the server, enable WOL to turn them on and NET RPC to shut them down. I have been doing this since ubuntu 12.04.  and this is the first time where I've had to reconfigure my scripts to make it work.

Here is a sample of the crontab on versions of Ubuntu Linux (before 26.04)

00 21 * * 1-4 $USER    $PATH/$Script.sh

My crontab is setup so at 9:00 pm on Monday though Thursday the script "$Script.sh" is run as $User that is located located at $PATH 

However in Ubuntu 26 it throws an error when running the script as the $USER, so once I removed the user from the crontab now looks like this.

00 21 * * 1-4 $PATH/$SCRIPT.sh

Terminal of Cron throwing an error


Created a log file to catch the error.  Add >> /$PATH/$LOGFILE.log to crontab


After looking at the log it is erroring out on the user?

Once the error is resolved


After troubleshooting and finding out that the user in the crontab was causing the error; I removed the user and crontab started running the scripts.  I was able to acknowledge that the script was running as the log filled up with the commands.  I was going though documentation for Ubuntu 26.04 and I either missed or I can't find the changes made in crontab.  It is interesting the little changes that though such a big monkey wrench into a system that really hasn't changed for years.  At any rate the issue has been resolved and the system is running the scripts as expected.

Monday, August 21, 2023

How to setup postfix on Ubuntu Server as a SMTP Email Relay

Setting up an SMTP Email Relay or Email Forwarder are used in organizations where applications that need to send email can where it is not dependent on an individual being logged in.  The typical example would be for email marking, but it can also be for the Photocopier in the office or any other number of commonly used devices that people use where it sends email.  The relay service allows you to use a generalized email setup by the organization.  Most commonly these are setup as "no-reply" or something to that effect.  To facilitate the setup of the mail forwarder/relay we will be using a Google Non-Profits email account.  The first thing you will need to do is setup the account, then login to the account and setup the account for use with "less secure app access".

Create the account, and set the password.  In this case I am using something called myemailservice


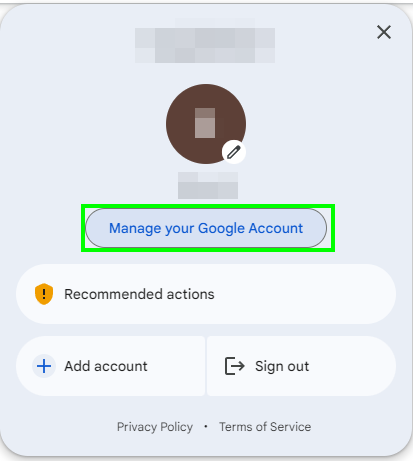
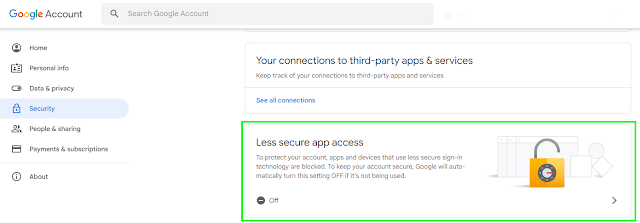
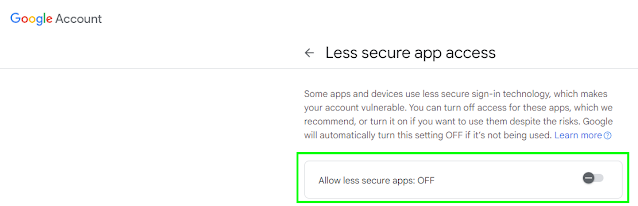
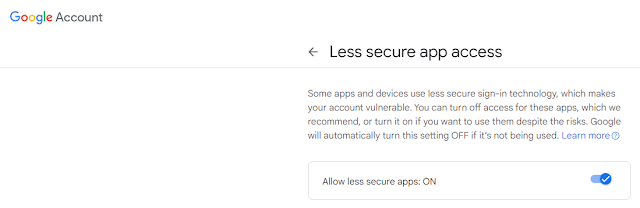
Then login to the account and setup "less secure app access" you can do this by using this link https://myaccount.google.com/lesssecureapps or by managing your Google Account as shown below.


Once that is done we can now do the setup for our relay server.  I am setting it up on Hyper-V using Ubuntu 22.04LTS.  I have given it 2 cores, a min 2GB Ram with dynamic memory management up to 8GB and a 40GB drive.  Obviously, networking, etc, etc, etc.  Also because it is linux don't forget to change the security boot setting to Microsoft Cert Authority.


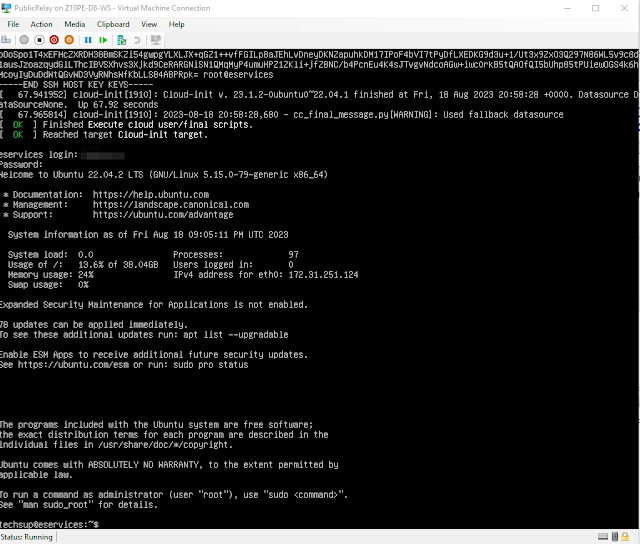
When installing Ubuntu Server I am going to do my typical setup; minimized, no GUI, Live patching, vim, Powershell and ssh access for the default install.

After installation login and update the system, and set your timezone.  By default ETC is typically used.  If you know your timezone like I do you can manually specify it.  

sudo timedatectl set-timezone America/Edmonton


To verify the setting use the command timedatectl or ls -l /etc/localtime


Now we will install our postfix smtp relay

Install Postfix

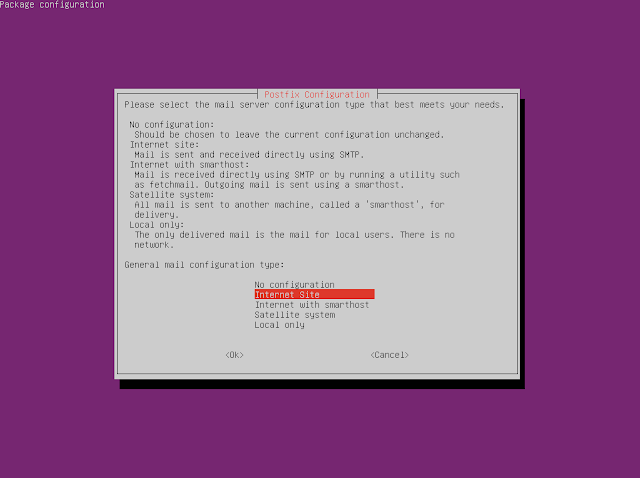
sudo apt-get install postfix and set the mail configuration to "Internet Site"


Postfix doesn't natively support SASL authentication so we must install a module for SASL authentication support.  You can read more about it here

https://www.postfix.org/SASL_README.html

 sudo apt-get install libsasl2-modules postfix mailutils


Once installed we need to configure post fix.

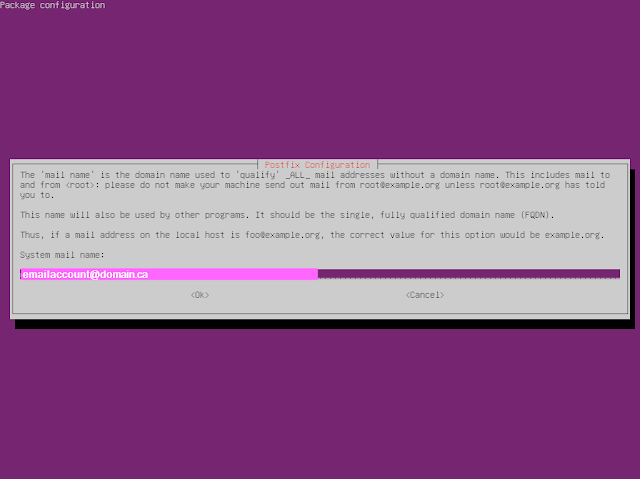
sudo vi /etc/postfix/main.cf and set myhostname to the FQDN


Then we need to add the following

relayhost = [smtp.gmail.com]:587

smtp_sasl_auth_enable = yes

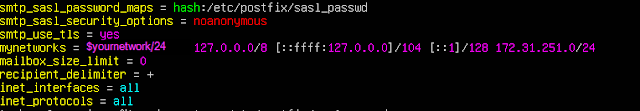
smtp_sasl_password_maps = hash:/etc/postfix/sasl_passwd

smtp_sasl_security_options = noanonymous

smtp_use_tls = yes


Also don't forget to add any networks you want to be able to send email from via smtp.  You will have to add the host or network range to the mynetworks variable as shown below.


Now we need to make our password map.  This will allow us to connect to the google account we are going to use to send the emails via smtp.  The file will be located in /etc/postfix/sasl_passwd

sudo vi /etc/postfix/sasl_passwd

in the file put the following

[smtp.gmail.com]:587 $youremailaccount:$accountpassword

and save and exit.

Change the permissions of the file so it is only readable by root

sudo chmod 600 /etc/postfix/sasl_passwd

restart postfix to apply our changes.

sudo systemctl restart postfix

To test our setting use the following 

echo "This is a test email body." | mail -s "Subject" -a "From: $fromemail@yourdomain.ca" youremail@domain.ca

I also use this depreciated powershell command for testing as well

Send-MailMessage -From '$fromemail@domain.ca' -To '$toemail@domain.ca' -Subject '$SomeSubject' -smtpserver 'DNS or IP to relayserver' -port '25'

Here are some important commands you will want to keep when using the relay server

postqueue - p

run all messages 

sendmail -q

get mail queue

postqueue -f 

flush the mail queue


Sources

https://support.google.com/accounts/answer/6010255?hl=en#zippy=%2Cif-less-secure-app-access-is-on-for-your-account

https://www.faqforge.com/linux/how-to-relay-email-from-postfix-mail-server-to-gmail-on-ubuntu/

https://www.cyberciti.biz/faq/how-to-configure-postfix-relayhost-smarthost-to-send-email-using-an-external-smptd/

https://www.tutorialspoint.com/configure-postfix-to-use-gmail-smtp-on-ubuntu

https://blog.iron.io/how-to-flush-a-postfix-mail-queue/

Wednesday, June 30, 2021

How to fix crontab scripts that won't run on Ubuntu 20.04

I've setup what I like to call WOLS (Wake on Lan & Shutdown) servers for a while now; 10 years to be exact.  They are very handy and require little to no system resources; I usually set them up on Hyper-V systems but have also done it on KVM and VMware.  It is very handy if your wanting to schedule systems for auto on and off without buying a commercial server or software.  You also don't have to have it connected to your domain if you don't want it to be.  

I setup a new server on Ubuntu 20.04 for managing the WOL/Shutdown for a remote location and set it up just as I have done in the past; but something was wrong.  It wasn't working.  The system was not turning on or shutting off the systems it was suppose to be.

For the purposes of this post lets say we are going to run all of our scripts out of /scripts/cron

You can use crontab -e or sudo crontab -e to edit cron, I prefer to modify the /etc/crontab file myself.  So when I build my WOLS server and modify the crontab file it usually looks something like this.

After I install the the required tools, WOL, samba tools, etc I white list the, WOL ports, SAMBA and remote desktop/Remote Access ports access though the firewall on both the client and the server. You can also disable the firewalls, though I don't recommend that.

The Startup Script is a shell script called startup.sh and it looks like this


I have found that if I don't put it in the arp cache I tend to have problems if the system has been off for a while.

sudo arp -i -s $IPADDRESS $MACADDRESS #COMMENT

example:

sudo arp -i -s $192.168.0.6 #FF:CC:DD:33:22:00

Then send the WOL Packets

sudo -i -u $SERVERUSER -p $PASSWORD wakeonlan -i $IPADDRESS $MACADDRESS #COMMENT

example:

sudo -i -u serveradm -p password wakeonlan -i 192.168.0.6 #FF:CC:DD:33:22:00

so you use the server usename and password to run the wakeonlan to the ipaddress with the specified mac address. The same is true with the shutdown script but you are using net rpc and you put in the windows client username and password behind the -U in quotes with a % separating the username and password as shown below.

The shutdown script is also a shell script called shutdown.sh and looks like this


sudo -i -u $SERVERUSER -p $PASSWORD net rpc shutdown -I $ipaddress -U "windowsclientusername%password" -t -1 -f 
sudo -i -u serveradm -p password net rpc shutdown -I 192.168.0.6 -U "joedirt%mopboy5" -t 1 -f
With that done, then adding execute permissions to the files and call it a day, as all the scripts worked when I manually executed them. Unfortunately that wasn't the case.  Something changed in Ubuntu 16 that caused files with extensions to not execute.

After troubleshooting and doing some Googling, I found this post with a similar issue to what I was having.  When I did a ls you can see the scripts in the folder.


With my files definitely having execute permission I tried the run-part command 
run-part --test /scripts/cron 
and got the following result


Nothing.  Absolutely nothing listed in the test.  So I did as Pete Fretag suggested and copied my startup.sh and shutdown.sh with out an extension.


Now the startup and shutdown scripts show up in the test.


When I run the scripts using sudo run-part /scripts/cron they also execute where they did not before.

Wednesday, May 05, 2021

How to upgrade your linux server

How do you do an in place upgrade on a older Linux Server and why would you want to.  Well why you would want to is obvious, security patches, and giving longer life to the server on the newer software; that is a good reason.  With browsers being constantly upgraded, along with security issues being found every other day it seems, staying up to date is just a good idea.

So how do we stay up to date?

Typically, if you have been staying up to date you will eventually get prompted to do an upgrade to an newer version of linux at some point.  All the following commands will need to be run as root (sudo).


sudo apt-get update

Downloads package information from all configured sources.  Running this command keeps your package information up-to-date

sudo apt-get upgrade

This command only upgrades.  The upgrades are only upgrades available to the platform, as defined in /etc/apt/sources.list or in /etc/apt/sources.list.d/.  This upgrades your packages, not your OS and it will not remove packages.

sudo apt-get dist-upgrade

Intelligently installs or removes packages as needed.  This command has a smart conflict resolution system.  The system attempts to upgrade the most important packages, at the expense of those deemed less important.  This command will also delete software if it is required to complete the upgrade process.

sudo apt-get autoremove

Removes packages that were automatically installed because another package required them but, if they are no longer needed this command removes them.

sudo apt-get autoclean

Clears the local repository of retrieved package files, but it only removes files that can no longer be downloaded and are virtually useless. It helps to keep your cache from growing too large

sudo do-release-upgrade

The do-release-upgrade command will upgrade the system from one release to another. This is the command you want if you want to upgrade from Ubuntu 18.04 to 20.04.  NOTE:  The system must be fully upgraded to run. use the apt-get upgrade, followed by sudo apt-get dist-upgrade commands before running the do-release-upgrade command.


Tuesday, December 11, 2018

Setting up and configuring a LAMP Server for Joomla

As a webdev, I spent a lot of time using projects such as xampp and wampp as a quick and easy way to start developing websites but have not had the chance to really deploy one myself, really besides the home server.  Even then I never really took the time to "Secure" the server properly and documentation for this is very wide ranging and opinionated at best.  There are lots of resources out there, but nothing that puts it into a nice neat package with any kind of explanation.  Most of the webservers I've used have been setup by other people, with little to no security in mind and why?  Because security is hard.  It breaks things, and it takes time to do it right.  In this post I will go over how to setup a secure web server from start to finish and this may be a good starting point for everyone who what to learn how to setup a secure server.  As always if you have any comments or pointer please do!

You can watch my video on setting up a Ubuntu 18.04.1 LTS Server on Microsoft Azure

https://www.youtube.com/watch?v=y9RQirmC_pk

This is my video of this post but with out really explaination of why I do some things.  It is just a start to finish this is how you setup the server.

https://www.youtube.com/watch?v=qszvUjjL-ZI

With our server already setup via Azure or even on our localhost though Hyper-V or KVM login into your server and update and upgrade any missing packages.


  1. Install Apache2

sudo apt install apache2


Once that is complete then we are going to install Mariadb


2. Install Mariadb

Add MariaDB Key

apt-key adv --recv-keys --keyserver hkp://keyserver.ubuntu.com:80 0xF1656F24C74CD1D8

Add MariaDB Repo

add-apt-repository 'deb [arch=amd64] http://mirror.nodesdirect.com/mariadb/repo/10.3/ubuntu bionic main'

update

sudo apt-get install mariadb-server mariadb-client

sudo mysql_secure_installation

Enter current password for root (enter for none): Just press the Enter

Set root password? [Y/n]: Y

New password: $password

Re-enter new password: $password

Remove anonymous users? [Y/n]: Y

Disallow root login remotely? [Y/n]: Y

Remove test database and access to it? [Y/n]: Y

Reload privilege tables now? [Y/n]: Y

sudo mysql -u root -p

$password


3. Create The Joomla Database


CREATE DATABASE $DBNAME;

Now here I would recommend creating a new user for the database we just created.

Create the User
create user $DBUSER

Grant privileges while assigning the password
grant all on $DBNAME.* to ‘$DBUSER’@’localhost’ identified by ‘$DBUSER_PASSWORD’


Note: The localhost field usually doesn’t have to be edited, but you can set it to the specific address. The above example grants all privileges, obviously. But you may want to limit privileges.

exit


4. Install Unzip

Install Unzip
sudo apt-get install unzip


5. Install PHP

Install PHP
sudo add-apt-repository ppa:ondrej/php
sudo apt update

sudo apt install php7.2 libapache2-mod-php7.2 php7.2-common php7.2-mbstring php7.2-xmlrpc php7.2-soap php7.2-gd php7.2-xml php7.2-intl php7.2-mysql php7.2-cli php7.2-zip php7.2-curl

if libzip error
vi /etc/apt/sources.list and add the following repositories

deb http://archive.ubuntu.com/ubuntu bionic universe multiverse
deb-src http://archive.ubuntu.com/ubuntu bionic universe multiverse
deb http://us.archive.ubuntu.com/ubuntu/ bionic universe
deb-src http://us.archive.ubuntu.com/ubuntu/ bionic universe
deb http://us.archive.ubuntu.com/ubuntu/ bionic-updates universe
deb-src http://us.archive.ubuntu.com/ubuntu/ bionic-updates universe
deb http://us.archive.ubuntu.com/ubuntu/ bionic multiverse
deb-src http://us.archive.ubuntu.com/ubuntu/ bionic multiverse
deb http://us.archive.ubuntu.com/ubuntu/ bionic-updates multiverse
deb-src http://us.archive.ubuntu.com/ubuntu/ bionic-updates multiverse
deb http://security.ubuntu.com/ubuntu bionic-security universe
deb-src http://security.ubuntu.com/ubuntu bionic-security universe
deb http://security.ubuntu.com/ubuntu bionic-security multiverse
deb-src http://security.ubuntu.com/ubuntu bionic-security multiverse

Then edit and make the following changes to the PHP INI File

sudo vi /etc/php/7.2/apache2/php.ini

file_uploads = On
allow_url_fopen = On
memory_limit = 256M
upload_max_filesize = 25M
max_execution_time = 360
date.timezone = America/Edmonton

Restart Apache

sudo systemctl restart apache2.service

Create the file phpinfo.php

sudo vi /var/www/html/phpinfo.php
<?php
phpinfo();
?>


6. Setup Virtual Hosts


Now that we have our apache server, mysql and php setup now we want to enable virtualhosts so we can host multiple websites on the same server.

In this configuration our default site configuration is located in /etc/apache2/sites-available we want to copy the default virtual host file called 000-default.conf contents to the new virtual host files like below.

sudo cp /etc/apache2/sites-available/000-default.conf /etc/apache2/sites-available/$myvirtualdomain.ca.conf

you would do this for however many sites you need, but I would recommend getting one setup first then copying the finished config as may times as you need using the command above.  Then edit and change the settings highlighted in yellow to suit what you need as many times as you need it.


Edit the virtual host file (sudo vi $myvirtualdomain.ca.conf)

# The ServerName directive sets the request scheme, hostname and port that

# the server uses to identify itself. This is used when creating

# redirection URLs. In the context of virtual hosts, the ServerName

# specifies what hostname must appear in the request's Host: header to

# match this virtual host. For the default virtual host (this file) this

# value is not decisive as it is used as a last resort host regardless.

# However, you must set it for any further virtual host explicitly.

#ServerName www.example.com

ServerAdmin demoadmin@domain.ca

ServerName webserver.domain.ca

ServerAlias www.domain.ca

DocumentRoot /var/www/html/domain.ca/public_html


# Available loglevels: trace8, ..., trace1, debug, info, notice, warn,

# error, crit, alert, emerg.

# It is also possible to configure the loglevel for particular

# modules, e.g.

#LogLevel info ssl:warn


ErrorLog ${APACHE_LOG_DIR}/error.log

CustomLog ${APACHE_LOG_DIR}/access.log combined


# For most configuration files from conf-available/, which are

# enabled or disabled at a global level, it is possible to

# include a line for only one particular virtual host. For example the

# following line enables the CGI configuration for this host only

# after it has been globally disabled with "a2disconf".

#Include conf-available/serve-cgi-bin.conf


Now disable the default config and enable your virtual host configuration files.

sudo a2dissite 000-default.conf - disables this config file

sudo a2ensite domain.ca.conf - enables config file of your virtual host you just setup.

you will have to restart apache for your setting to take effect.

sudo service apache2 restart


***NOTE it is very important that the ServerAlias matches the DNS otherwise the virtual host will not redirect the browser properly.

If your working locally, you can make changes to your local hosts file.  Once you've gotten everything setup you can make changes to the DNS for Production.


7. Copy Joomla to the Webserver

Now upload the latest version of Joomla to the server via SCP.  Make sure you have a writable directory you can save to if you don't make one.

SCP /path-to-file/file.zip $username@$HOST:/path-to-destination-folder/


in this case I typically use just the home directory


SCP /path-to-file/file.zip $username@$HOST:/~/file.zip


Then copy and paste the zip file to the virtual host directory we created for the site.


sudo cp Joomla_X.X.X-Stable-Full_Package.zip /Path/To/Virtual/Site


Once copied to the server move it to the /var/www/html/$site virtual directory we just enabled and unzip the file.

Run unzip sudo unzip Joomla_X.X.X-Stable-Full_Package.zip

The default settings in Joomla are a little different from what however before we do that you will want to fix a couple settings in your php.ini file.

There are 2 things we need to fix.  Now for Joomla, recommended settings are to disable output buffering, to do that we need to edit the php.ini file

sudo vi  /etc/php/7.2/apache2

Find
output_buffering = 4096
and change it to Off
output_buffering = Off

while were here we are going to increase the max file upload size

Save your changes restart apache

With the file now unzipped we are going to add our user/owner to the www-data group so we can properly run and execute Joomla.

By default the www-data user and group are unprivileged; however Joomla requires the www-data group to have certain permissions.  So we are going to add the owner of the files to the www-data group so that Joomla can install modules, run updates, etc.  We don't want to set ownership of any files to the www-data user. The whole point of the www-data user is that it is an unprivileged user, not able to write to any files. Server daemons accessible from the outside network (such as the web server) typically run as an unprivileged user so that in the event that they are hacked due to a vulnerability, the possible things the attacker can do is minimal. In these cases you should set ownership to www-data ONLY for those files, keeping the number of files writable by www-data at a minimum it's the same reason, don't set any files to be world-writable.  You need to give www-data write permission to the joomla directory files. We don't want to give www-data ownership because of the security implications.  So to do this we are going to add our user to the www-data group, which will  give Joomla the permissions we need for it to run.

add $USER to www-data

sudo usermod -a -G www-data $USER

sudo chgrp -R www-data /var/www/html/$Site
sudo chown -R www-data:$USER /var/www/html/$Site

Do this for the setup then change your files and folders for

If you want to re-verify the proper permissions on the files and folders run the following commands

find /var/www/html/$Site -type d -exec chmod 755 {} \;
find /var/www/html/$Site -type f -exec chmod 644 {} \;

Logout and log back into to verify the changes were made.  Now you should be able to run the Joomla installer without any write or execute permission issues.

Now open your browser and run though the Joomla setup.  http://yournewjoomlasite/index.php


Enable .htaccess and security headers

To enable .htaccess and security headers you will need to add the following to your Site Config file located in /etc/apache2/sites-available called $Site-Domain.conf

Add the following just under the tag

Options Indexes FollowSymLinks
Options FollowSymLinks
AllowOverride ALL
Require all granted


Save the config file then eneable a2enmod by
sudo a2enmod rewrite
then restart apache
sudo systemctl restart apache2


Securing The Webserver

enable module headers

sudo a2enmod headers

Now edit the security.conf file typically localed in  /etc/apache2/conf-available/security.conf

Header unset X-Powered-By
Header always unset X-Powered-By
Header edit Set-Cookie ^(.*)$ $1;HttpOnly;Secure - Enable once you have ssl setup.
Header set X-Permitted-Cross-Domain-Policies "none"
Header always set X-XSS-Protection "1; mode=block"
Header always set x-Frame-Options "SAMEORIGIN"
Header always set X-Content-Type-Options "nosniff"
Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains"
Header always set Feature-Policy "microphone 'none'; payment 'none'; sync-xhr 'self' Header always set Referrer-Policy "strict-origin"

<!--very secure policy--!>
Header always set Content-Security-Policy "default-src 'self'; font-src *;img-src * data:; script-src *; style-src *;"

Very Insecure policy if your going to be using several different joomla extensions.

Header always set Content-Security-Policy "default-src 'self'; connect-src *; font-src *; frame-src *; img-src * data:; media-src *; object-src *; script-src * 'unsafe-inline' 'unsafe-eval'; style-src * 'unsafe-inline';"

So if you want a copy paste security headers

Header unset X-Powered-By
Header always unset X-Powered-By
#Header edit Set-Cookie ^(.*)$ $1;HttpOnly;Secure
Header set X-Permitted-Cross-Domain-Policies "none"
Header always set X-XSS-Protection "1; mode=block"
Header always set x-Frame-Options "SAMEORIGIN"
Header always set X-Content-Type-Options "nosniff"
Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains"
Header always set Feature-Policy "microphone 'none'; payment 'none'; sync-xhr 'self' Header always set Referrer-Policy "strict-origin"
Header always set Content-Security-Policy "default-src 'self'; connect-src *; font-src *; frame-src *; img-src * data:; media-src *; object-src *; script-src * 'unsafe-inline' 'unsafe-eval'; style-src * 'unsafe-inline';"

then restart apache

sudo systemctl restart apache2


Disable Expose PHP

sudo vi /etc/php/7.2/apache2/php.ini

expose_php = Off

Setup your domains and DNS

Now before we setup our SSL Cert, we need to setup our DNS.  For my DNS I needed to setup both an A record.


Now once the DNS resolves we can setup our SSL Certificate using Let's Encrypt.

Setup the SSL Certificate

Digital Ocean has a great post on setting up Let's Encrypt on Ubuntu.  You can get the source link in the resources.

Step 1 - Add the repository and install Certbot

sudo add-apt-repository ppa:certbot/certbot

Install Certbot's Apache package with apt:

sudo apt install python-certbot-apache


Step 2 - Set Up the SSL Certificate

Verify that the Server name matches the domain name your going to use.  If it doesn't change it so it matches.

sudo vi /etc/apache2/sites-available/$SITE.conf

Your server name should match the domain your setting up with lets encrypt.
ServerName YOURDOMAIN.CA; 

You can verify the syntax of your configuration edits:

sudo apache2ctl configtest

If you get an error, reopen the virtual host file and check for any typos or missing characters. Once your configuration file's syntax is correct, reload Apache to load the new configuration:

sudo systemctl reload apache2

Certbot can now find the correct VirtualHost block and update it.

Step 3 - Allowing HTTPS and SSH Through the Firewall

You can see the current setting by typing:

sudo ufw status

sudo ufw allow 'ssh'
sudo ufw allow 'Apache Full'
sudo ufw delete allow 'Apache'

if it is disabled do a sudo ufw enable to enable the firewall

Your status should now look like this:

sudo ufw status
Output
Status: active

To                         Action      From
--                         ------      ----
OpenSSH                    ALLOW       Anywhere                  
Apache Full                ALLOW       Anywhere                  
OpenSSH (v6)               ALLOW       Anywhere (v6)             
Apache Full (v6)           ALLOW       Anywhere (v6)        


Step 4 - Obtaining an SSL Certificate
Certbot has an Apache plugin that will take care of reconfiguring Apache and reloading the config whenever necessary.

sudo certbot --apache -d domain.ca -d dev.domain.ca
This runs certbot with the --apache plugin, using -d to specify the names you'd like the certificate to be valid for.

The first time you run certbot, you will be prompted to enter an email address and agree to the terms of service. After doing so, certbot will communicate with the Let's Encrypt server, then run a challenge to verify that you control the domain you're requesting a certificate for.

If that's successful, certbot will ask how you'd like to configure your HTTPS settings:

Example:

Please choose whether or not to redirect HTTP traffic to HTTPS, removing HTTP access.
-------------------------------------------------------------------------------
1: No redirect - Make no further changes to the webserver configuration.
2: Redirect - Make all requests redirect to secure HTTPS access. Choose this for
new sites, or if you're confident your site works on HTTPS. You can undo this
change by editing your web server's configuration.
-------------------------------------------------------------------------------
Select the appropriate number [1-2] then [enter] (press 'c' to cancel):
I would suggest selecting option 2.  The configuration on you server will be updated, and Apache will reload to pick up the new settings. certbot will wrap up with a message telling you the process was successful and where your certificates are stored:

Example:
IMPORTANT NOTES:
 - Congratulations! Your certificate and chain have been saved at:
   /etc/letsencrypt/live/example.com/fullchain.pem
   Your key file has been saved at:
   /etc/letsencrypt/live/example.com/privkey.pem
   Your cert will expire on 2018-07-23. To obtain a new or tweaked
   version of this certificate in the future, simply run certbot again
   with the "certonly" option. To non-interactively renew *all* of
   your certificates, run "certbot renew"
 - Your account credentials have been saved in your Certbot
   configuration directory at /etc/letsencrypt. You should make a
   secure backup of this folder now. This configuration directory will
   also contain certificates and private keys obtained by Certbot so
   making regular backups of this folder is ideal.
 - If you like Certbot, please consider supporting our work by:

   Donating to ISRG / Let's Encrypt:   https://letsencrypt.org/donate
   Donating to EFF:                    https://eff.org/donate-le

Your certificates are downloaded, installed, and loaded. Try reloading your website using https:// and notice your browser's security indicator. It should indicate that the site is properly secured, usually with a green lock icon. If you test your server using the SSL Labs Server Test, it will get an A grade.

Let's finish by testing the renewal process.

Step 5 - Verifying Certbot Auto-Renewal

Let's Encrypt's certificates are only valid for ninety days. This is to encourage users to automate their certificate renewal process. The certbot package takes care of this for us by adding a renew script to /etc/cron.d. This script runs twice a day and will automatically renew any certificate that's within thirty days of expiration.

To test the renewal process, you can do a dry run with certbot:

sudo certbot renew --dry-run


If you see no errors, you're all set. When necessary, Certbot will renew your certificates and reload Apache to pick up the changes. If the automated renewal process ever fails, Let’s Encrypt will send a message to the email you specified, warning you when your certificate is about to expire.

Security Tests and Scanners

https://app.upguard.com
https://pentest-tools.com/
https://sitecheck.sucuri.net
https://hackertarget.com/
https://www.owasp.org/index.php/Category:Vulnerability_Scanning_Tools
https://securityheaders.com/
https://tools.geekflare.com/report/header-security-test/
https://app.upguard.com/webscan#/
https://qualysguard.qg3.apps.qualys.com/fo/home/Dashboard.php?skip=1
https://pentest-tools.com/website-vulnerability-scanning/web-server-scanner#
https://observatory.mozilla.org/


Browser addons

https://chrome.google.com/webstore/detail/csp-evaluator/fjohamlofnakbnbfjkohkbdigoodcejf
https://addons.mozilla.org/en-US/firefox/addon/laboratory-by-mozilla/


References

Setting up a lampp server
https://websiteforstudents.com/installing-apache2-mariadb-on-ubuntu-16-04-17-10-18-04-with-php-7-2-support-lamp/

Configuring Virtual Hosts
https://www.ostechnix.com/configure-apache-virtual-hosts-ubuntu-part-1/
https://httpd.apache.org/docs/current/vhosts/

Server Hardening
https://askubuntu.com/questions/778463/www-data-vs-username
https://stackoverflow.com/questions/9133024/www-data-permissions/19620585#19620585
https://unix.stackexchange.com/questions/268905/is-giving-all-permissions-to-www-data-group-a-good-idea
https://www.tecmint.com/hide-apache-web-server-version-information/

.HTACCESS
https://www.opentechguides.com/how-to/article/apache/115/htaccess-file-dir-security.html

adding user to www-data group & Joomla Security Checklist
https://www.cyberciti.biz/faq/ubuntu-add-user-to-group-www-data/
https://docs.joomla.org/Security_Checklist/Joomla!_Setup
https://docs.joomla.org/Security_and_Performance_FAQs

Security Headers
https://kb.sucuri.net/warnings/hardening
https://www.ryadel.com/en/apache-setup-httpd-conf-file-send-http-security-headers-web-site/
https://jsblog.insiderattack.net/apache-security-configuring-secure-response-headers-e8a83b72ce5e
https://geekflare.com/apache-web-server-hardening-security/
https://geekflare.com/httponly-secure-cookie-apache/

Setup SSL
https://www.digitalocean.com/community/tutorials/how-to-secure-apache-with-let-s-encrypt-on-ubuntu-18-04


Removing Show Recent History and Recently Open Documents from Windows Explorer

How to remove the Recent History and Recently Open Documents from Windows Explorer Using the Registry Editor Press the Windows Key + R, type...