Showing posts with label MDM. Show all posts

Thursday, April 28, 2022

Google EMM Update Causes Organization Email Issues on Android

Before looking into the google admin issue I thought it was a problem with my device and wiped it clean, after that didn't work I looked into google admin for google workspaces.  

Here is some background on how the EMM provider was being used before today.  The EMM provider was setup to use with organization purchased devices, and the organization did not want to associate personal devices with the EMM provider (meraki in this case) and the changes google has made to their policy won't allow you to use Google for Staff (personal) devices and the EMM provider for organizational devices.  It seems that google now throws everything to the EMM provider if you have your domain associated with one.

I had to remove the EMM provider from the organization otherwise it was treating the device as an organizational purchased device.  When Google has made to Google Workspaces EMM Provider this caused Android devices in the organization to lose access to their Work Email. 

The organization requires data access control on devices so the only way I could get this to work was to embrace google work profiles; which isn't the best user experience but is the only way I could get this working. Google sent a notice in 2017, about the EMM Provider changes but a reminder about the coming changes would have been nice.

In an email to google about the issue, they replied with the following.

Thank you for contacting Google Workspace Support. This is ****** and I will be assisting you about how to fix the sync error you are encountering due to the old Device policy app that you are still using for your Android device. It is a pleasure assisting you. 


Before we begin I would like to set the proper expectations about our new Android Device Policy app that replaced the Google Device Policy app. There is current known issue about the new Android Device Policy app that is still being checked by our Product Engineers, about a possible limitation of some Android Devices that cannot install the new Android Device policy app. And even if the app was installed, the Android device just could not be managed or simply said, the Android Device Policy app is not compatible with the Android device.

However, in order to fix the sync issue these are the steps to follow.

Resolution: If the device is for work and personal use:
Re-register your device by removing your work profile and then adding back your Google Workspace account and work profile. 


  • Open your device settings. 
  • Tap Accounts and then Remove work profile.
  • Tap Delete to confirm.
  • Go to I’m using my own personal device and follow the steps to add your Google Workspace account and work profile.
  • Assisted how to uninstall Device Policy app and install Android Device Policy app.
  • remove Workspace Profile.
Next steps:

How do I switch to the Android Device Policy from the Google Device Policy app?
If your device is for work and personal use and it "has a work profile":
  • Remove the work profile.
  • Open the Settings app and tap Accounts.
  • Add the work account again and set up Android Device Policy.
  • (A work profile is required for Android Device Policy.)

My device is for work and personal use and "doesn’t have a work profile":
  • Open the Google Apps Device Policy app.
  • Tap Unregister.
  • The work account is removed from the device.
Open the Settings app and tap Accounts.
  • Add the work account again and set up Android Device Policy.
  • During enrollment, you must set up a work profile because it's required for Android Device Policy.

Please check this help article for reference for the above steps: 

About Android Device Policy: https://support.google.com/a/users/answer/9453213


If you have an issue on a Tablet that simply is not compatible with the Device Policy app. The only option we have is to change the Mobile management for Android Device. You currently have a Custom Mobile Device management that is set to Advanced. You can change this to Basic, the good thing about this is the Android Device Policy app is no longer needed. And this will simplify your log ins to any Device similar to your iOS devices.

To change the Mobile Device management to Basic:
From the Admin console > click Devices > Mobile &endpoints > Settings > Universal settings.
On the next page > click General > Mobile management > change Android Mobile management to Basic. Please note: Only do this, if you believe you have no real need of the Advanced Mobile management option for your Android devices.

Here are some helpful link(s) that you can use:

Set up basic mobile device management: 
https://support.google.com/a/answer/7400753

We value your time and effort in contacting us. That is why, I'm keeping this case open. If our resolution does not work, kindly reply to the email and provide me your phone number and best time of call, so that I can work further with you on this. It's either we can do a screen sharing session or if you send me a video or screen shot of the error that will help me identify the issue. This case will remain active and can be reopened within 30 days.


If there are other concerns aside from what we've discussed, our main priority is to provide the best support experience, with this in mind, if you need assistance during this time feel free to reply to my email or call us or initiate a chat session for immediate help and this is the link for reference https://support.google.com/cloudidentity/answer/7668654 . We have 24/7 support and any of my colleagues will be glad to help.

Don't forget to generate a PIN should you give us a call. You can refer to this article for instructions on how to do so https://support.google.com/a/answer/60233.

Thank you for choosing Google Workspace and have a wonderful day.

Sincerely,
 

*****
Google Workspace Support


Here are some additional information linked below

https://www.blog.google/products/android-enterprise/da-migration/
https://developers.google.com/android/work/device-admin-deprecation


To resolve the issues I removed the EMM provider so google workspaces would handle the MDM for android; as there can't really have a separation of the two anymore it seems.
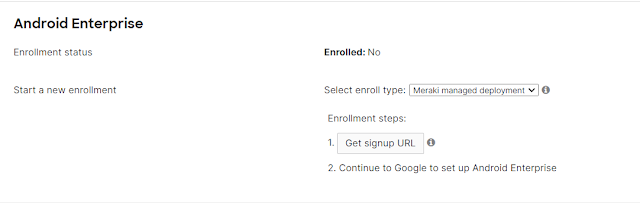
So in the MDM (Meraki) I removed android enterprise from the google domain, so android devices are just managed by google workspaces.


Once that was done after a few minutes I was able to start to get my work profile working correctly from google by adding a work profile.  Here are the universal settings for how android devices are setup.

Universal Settings

You must ensure that work profile setup is enable on in your Android Settings


For users to connect their android devices they require a work profile. This will be slightly different for every android device but the steps would be relatively the same.

Remove your current work account from your device, Please note that you will only be able to have one work account associated with a device at a time (so if you need other accounts you will have to find a work around)


1 - Add the account by pressing the arrow next to your name and email.


2 - Select "Add another account".


3 - Select Google for the Account.
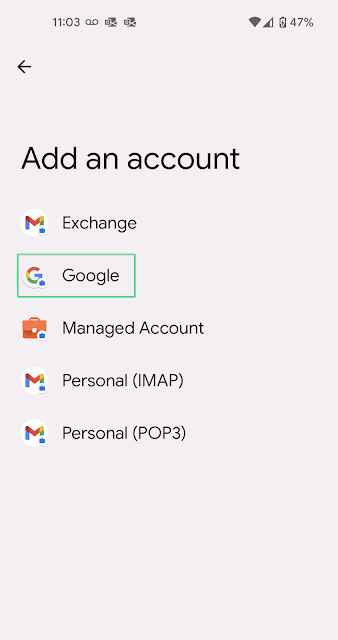


4 - Enter in your Email and Password


5 - Accept the Terms Of Use


6 - Install Google Device Administrator


7 - Press Install
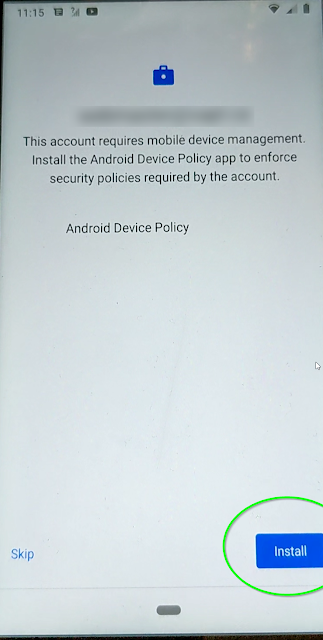


8 - Create your google work profile. It will take about 5 to 10 minutes to create the work profile.  So Please be Patient.


Setting up google work profile


Screen after accept and continue


Almost Finished


When it is finished it should show you the added account.


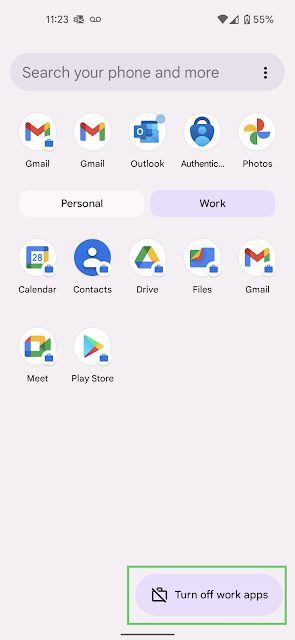
Now you will have two different apps. Work Apps and Personal Apps.


Personal


Work


Work apps are shown by the little briefcase on the app.


Work apps can be paused (turned off) which will stop notifications from reaching you which can be enabled or disabled from the apps drawer.


In your Gmail app you can switch from personal and work email easily but you have to go from the account icon in the top right to switch.


I understand why google set things up like this; putting the separation between work and personal settings, making it easier to wipe devices, and remove access, etc.  It isn't as "user friendly" as I would have liked it to be and it will be a transition for some users.

Friday, October 22, 2021

Meraki MDM - Fixing Invalid Profile when adding device to MDM

 With apple's iOS 15 update, I found I had some issues to fix with some of our organizations iPads, specifically because they are only 16 gb versions; they were out of space.  Also with the pandemic the Push cert was not kept up due to the systems being off.  Resetting and reformatting the ipads ended up being required.  Now these ipads were store bought ipads and not directly purchased from apple; which complicates things.  That caused the ipads to no longer connect to the Meraki MDM due to the bad push certificate and when I tried to re-add them using Apple Configurator 2, I got the invalid profile error.


After a lot of pain and troubleshooting, I had managed to make some progress on getting these ipads re-set up on the Meraki MDM.  After updating them to iOS 15.0.2 I ran the apple configurator which put them in the Apple Business Management center, but would not configure the ipads for use with the MDM.  

An issue that I also found which was causing me some of the grief is these ipads were somehow added to an icloud account, which I need to be removed before I could continue.  After removing the ipads from the iCloud account, I setup the ipads for automated enrollment thought Apple Configurator 2.  Doing this put the ipads into Apple Business Manager but still would not configure the ipads to use the MDM with the push certificate.  

I thought I would try and add them to the Meraki DEP, which I was able to do but this did not help me with getting the ipads setup to be used and updated with the push certificate.  What ended up being the solution was resetting all the certs (again), and setting up the ipads for just supervision with no MDM.  After the iPads were Supervised I was apple to add them to the MDM using Safari and the MDM web link.  I also had to remove the education configuration part of a profile configuration


 I thought this was odd but it was causing the following two errors in the Meraki log which you can see below.

Error: The top-level user “xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxx” is neither a leader nor a member.

Error: The payload “Your Meraki iPad Profile” is invalid.


Ultimately I re-did all the certs between apple business manager and Meraki
  • The Apple configurator certificate
  • the VPP certificate
  • the push certificate
  • DEP certificate.  
Then I removed the education part of the profile and setup the ipads as just supervised devices with no MDM having to add them manually after.   This worked and got the ipads back up in working order.

Connect the ipads to your mac and open Apple Configurator 2 and select the ipad or ipads and select the Prepare


Select Supervise devices and allow devices to pair with other computers.


Select do not enroll in MDM


Select the Organization 


Configure iOS Setup


After the ipad has been supervised, the ipad could be connected to the internet.

Un-Supervised Device

Once the ipad was supervised, the wifi screen shows up and when connected can then be joined to the MDM by the enrollment URL/Link.  You must use safari to connect to the MDM.

iOS Screen

I was able to use safari get to the enrollment URL/Link to join the MDM and the profiles were applied right away.  However before you do if you have apps that you will want to use that were purchased on a specific profile you will have to sign into the ipad with that account before loading the MDM.  Otherwise you will lose access to those apps.

Meraki Network Registration

 
Sign in with Google

Sign in with a Meraki email.

Enter the password

Finds The MDM Network

Allow the profile to download to the iPad

Close the alert and open the settings


Click on Profile Downloaded

Install the profile


Trust the certificate from the MDM


Once the profile is installed, the ipad will start reconfiguring to what you have setup for the profile on the MDM.


to get the devices setup.  Once that was done.  I used apple configurator to just supervise the devices.  Then I used safari to add them to the MDM.  Once there I was able to set them up as before in Meraki, adding and removing profiles as required for apps.


Tuesday, July 02, 2019

How to renew the Apple Push Certificate for Cisco Meraki MDM

With Apple equipment when used with a MD such as Cisco meraki you have to update your push certificate every year otherwise your connection between the devices and your MDM will break and then you will be doing manual updates until you get the devices reset with your MDM.  Here is how you update your apple push certificate to your apple devices before the expiration date so you don't lose the connection between your MDM and your apple devices.


1 - Login to your Meraki MDM


2 - Select MDM Network -> then under the Organization menu under "Configure" select MDM


3. Once here select the Update/Renew Certificate button.


4.  Download your CSR File.  If you don't keep a clean house (or download folder) note the name and date of the file as it is very important.  In my case it is "Meraki_Apple_CSR (4).csr"


5. Then click on the link for the Apple Push Certificate Portal and login with the ID you are going to use or using with the MDM.  (It is the ID is tied to the CSR) so in this case mdmaccount@domain.ca.  Don't forget that you will need your 2FA device to be able to login.


6.  Select Renew on the Certificate you want to renew.  Then upload the CSR; this is the file from step 4 - "Meraki_Apple_CSR (4).csr"


7.  Then once done you will download your new Certificate to use with your MDM.  Again make note of the name and date if you don't keep things tidy.  In my case it is "MDM_ Meraki Inc._Certificate (1).pem" 


8. Now go back to your meraki mdm and enter in the email address and upload the certificate we got from apple (MDM_ Meraki Inc._Certificate (1).pem


9. Save the settings (this is usually on the bottom of the page or on the bottom right)

10.  Now your certificate expiry should be from 1 year as shown below


You can view a youtube video of the process here


References:

Removing Show Recent History and Recently Open Documents from Windows Explorer

How to remove the Recent History and Recently Open Documents from Windows Explorer Using the Registry Editor Press the Windows Key + R, type...