Showing posts with label PFSense. Show all posts

Thursday, March 21, 2024

How to migrate PFSense Over to KEA DHCP Server from ISC DHCP Server

I am a PFSENSE User and I manage PFSENSE for some other organizations and the time has come to make the switch for the DHCP Server over to KEA from ISC.

Why switch to KEA from ISC?

  • ISC will no longer be supported
  • KEA has some nice High availability features for IPV4 & IPV6
  • Robust Host Reservations which are per subnet vs global, but global reservations are supported.
ISC has some documentation and tools for migrating over to KEA from ISC.  PFSense has a warning on the firewalls which can be ignored at your own peril.


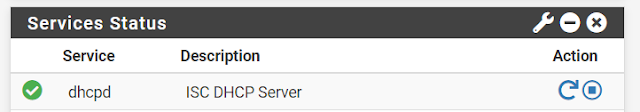
Now in PFSense if you try to just "switch" over you may encounter an error.  You can see that my ISC Server is running fine but when I switch over to KEA DHCP "Breaks"


The issue is caused by the NTP Server settings in the DHCP Server, not sure why they are there, perhaps if you wanted to setup your own linux NTP server or something for time syncing or an AD Server then you could just put in the IP of the machine.  Still with how you now setup NTP in PFSense it seems a little redundant to have that there.  At any rate you need to either remove the NTP DNS server settings from the DHCP server settings unless they are an IP address.  So for myself I setup the NTP server to the localhost 127.0.0.1 or the main ip or you can do both.  


With that setup we can modify our NTP server in PFSense located under services


It is recommended setting up 3 to 5 ntp servers to sync with.  For myself I decided to go with

  1. time.apple.com
  2. time.windows.com
  3. time.google.com
  4. time.cloudflare.com
  5. time.nist.gov
I have set time.apple.com and time.windows.com as my preferred NTP Servers


With that setup and done, I ssh'd into my firewall to check the time.  

I ran the command date +"%T" 


and when you check the general setting for the time servers you see the NTP Servers we setup in our NTP Service


With these settings your KES migration should be complete and the DHCP Server should work flawlessly.  I had no issues with the migration once I removed my NTP servers using DNS.  Time has been in sync with no issues.


Tuesday, March 01, 2022

Restore a PFSense Backup using the CLI (Command Line Interface)

This tutorial will go though how to restore a PFSense Configuration though the Command Line Interface (CLI).  You will need a few things before we begin.

  1. A usb drive formatted as FAT32
  2. A backup of your PFSense Config File on the thumb drive.


Once that is done, and you have your fresh version of PFSense installed and ready to go.


plug your USB device into the system.


We see the device is da0, but we will run camcontrol with devlist to verify the USB Drive to do that we will need to enter shell mode by selecting option 8


Then we will run the command 
camcontrol devlist


We can see that da0 is our usb drive, so to see all available partitions we will run 

ls /dev/da0*

So we can see a single partition /dev/da0s1 so we need to mount it.  To mount it we will need to make a folder to mount to.  In this case I'm going to make a folder called bak

mkdir /media/bak


then using the following command to mount the usb drive to /media/bak

mount_msdosfs /dev/da0s1 /media/bak


Then we are going to cd into /media/bak and run a ls to see what files we have on the drive

cd /media/bak

LS 


We find our pfsense backup file now we will copy it to /cf/conf/config.xml overwriting the default config file.  If you so choose you can make a backup of the default config by first doing
 cp /cf/conf/config.xml /cf/conf/config.bak

I am just going to overwrite the file. To do that I am going to run

cp /media/bak/mypfsensebackup-20220228051431.xml /cf/conf/config.xml

This will copy/paste the backup file into the /cf/conf directory and rename the file to config.xml overwriting the file that is currently there.


Now we will remove the temp file and reboot the system.

rm /tmp/config.cache


exit shell 

exit

then select option 5 and reboot


Once you have rebooted your configuration should be applied if there were no issues or compatibility issues.


Tuesday, November 09, 2021

Setting up Dynamic DNS with PFSense and GreenGeeks Web Hosting

One of the things I have been struggling to setup in the last few years was a reliable way of setting up my Domain DNS with my home internet connection.  My ISP (Telus) assigns dynamic IP address, which is typical for many home internet connections.  I was using ddns to handle my vpn url, however reciently I missed the renewal email and I hadn't bothered to set something new up.  I have a greengeeks webhosting account, and use PFSense as my home firewall/router so I decided to have a look at the settings and see what I can setup with the two of these.

The first thing you will want to do is setup the DNS on your GreenGeeks account.

1. Go to Dynamic DNS when you enter the CPANEL


2. Create a new entry


3. Fill Out all the relevant information.  So a good example for this might be vpnconnect.yourdomain.ca where vpnconnect is the subdomain and yourdomain.ca is the domain selected.  You can manually enter in your ip from your firewall here I left mine blank and will be propagated once the URL is put into the PFSense Firewall.


Once Created.  Copy the Dynamic DNS URL, we will need to put it into our PFSense Firewall.


Login to PFSense go to Services -> Dynamic DNS

1. Setup Dynamic DNS


2. Press the + Add Button


3. Select the Service Type to "Custom" and both interfaces should be set to "WAN"


4. Enter in your username and password for your cpanel account.


5. Enter in the URL for updating your Dynamic DNS.  We copied the URL from our Dynamic DNS Settings in the CPANEL


Once you hit SAVE, the firewall should update and your IP will display in the webhost CPANEL and on your PFSense Firewall.  If the IP is green then everything is good, if it is red, then it is not working properly.


Monday, December 23, 2019

Setting up a site to site VPN on PFSense using OpenVPN

How to setup a site to site VPN on PFSense using OpenVPN.

The organization I work for is expanding so we investigated if it would be possible to get a fiber connection to our head office.  Fortunately that is not possible so we went with business level internet with a static IP on Telus Fiber 300mbps (we need a good up stream). 

Which means we need a VPN (Dramatic sound effect).  The last time the organization did a VPN it did not go well, the connection was slow, laggy and barely functional (I think it was mostly the internet connection - we resolved it by using RDP).  However that was then and this is now.  I was asked to see if we could get something going using PFSense, since I setup the OpenVPN server for our client remoting, and it has worked really well, I looked into using OpenVPN for a site to site.  Lawrence Systems has a great video on how to do this as did Crosstalk solutions.  I used both for reference as the network I was working with wasn't a typical setup.  This post I hope will be useful for those trying to do a site to site VPN from a satelite/branch location and having to communicate with the main location.  Below is a overview diagram of how this essentially works.


Overview Diagram


In PFSense the server part for you main/master location is very simple to setup.  You essentially have to setup 3 main things.


  1. The VPN connection to go back to the satelite/branch location's network
  2. Configure firewall rules to allow the VPN connection with proper routing
  3. Configure openvpn firewall rules to allow for the connection.
1.1 Configure General Settings
OpenVPN General Information Settings
 1.2 - Configure Cryptographic Settings
I recommend using all default settings here and adjusting after the fact.  Depending on your system and adjusting them after you have the connection established if you require more security.

OpenVPN Cryptographic Settings
1.3 - Tunnel Settings
The IPv4 Tunnel network need to be the same ip range on the client firewall as the server firewall.  It is the virtual network that allows the traffic to go from the firewalls to transverse to the other locations networks
The IPv4 Remote network is the network you are trying to reach on the other side's firewall so since this is the server setting, we want to put the ip network of the client firewall we are trying to reach. In this case 192.168.96.0/24 which is the network at the remote site.
Server Tunnel Settings


1.4 - Advanced Configuration
You can put any custom configuration here increase your logging level for troubleshooting.
Advanced Configuration

Firewall Rules:


WAN: - The protocol should just by udp ip4 with the source coming from your public IP provided by your ISP and the port number you have set to use on your firewall for the openVPN server

WAN Firewall Rules
WAN Firewall Rules
OpenVPN: - is typically left wide open unless you want to lock it down yourself.

OpenVPN Firewall Rule

OpenVPN Firewall Rule

For the client on the other hand there is a bunch of setup that has to be done, especially if you want to reach other networks.

Setup an OpenVPN client in PFSense

OpenVPN Client to connect the 2 firewalls
PFSENSE OPENVPN Client Settings


OpenVPN Cryptographic Settings (Should be the same as the server)

Client Tunnel Settings
The IPv4 Tunnel network need to be the same ip range on the client firewall as the server firewall.  It is the virtual network that allows the traffic to go from the firewalls to transverse to the other locations networks
The IPv4 Remote network is the network you are trying to reach on the other side's firewall so since this is the server setting, we want to put the ip network of the client firewall we are trying to reach. In this case as with the overview diagram 192.168.1.0/24, which is the network at the main office.  If you have more then one network you want to reach add a comma to the remote networks such as 192.168.1.0/24, 172.19.4.0/24 and if you have the firewall/nat rules in place you should be able to reach both networks.
Client Tunnel Settings


Pushing DNS

On my client firewall I am using DNS resolver, which allows me to specify specific domain lookup servers.  My DNS resolver is setup to use DNS over TLS, so I added a domain override for domain specific lookups for my specific domain.  This is especially useful in an active directory environment.

Domain Specific lookups
Again you have to ensure firewall rules are setup for your client firewall much like your server firewall to allow the OpenVPN traffic though to the proper networks.

Firewall Rules:


WAN: - The protocol should just by udp ip4 with the source coming from your public IP provided by your ISP and the port number you have set to use on your firewall for the openVPN server

WAN Firewall Rules
WAN Firewall Rules
OpenVPN: - is typically left wide open unless you want to lock it down yourself.

OpenVPN Firewall Rule

OpenVPN Firewall Rule

How to make google calendar more secure

With the rash of spam and phishing attempts lately, I would recommend making the following changes to your google calendar settings to secur...